Summary
Employees may understand security policies yet still take shortcuts when approved processes make their jobs harder. Drawing on his experience at Sweden's Transport Agency and Örebro Municipality, information security expert Tobias Ander explains how unsafe practices become normal, why managers' responses to reported problems matter and what HR can do to help improve cybersecurity culture.
I once asked why a recurring security deviation was not being reported. The answer came quickly: “Everyone does it all the time. If we reported every case we would do nothing else.”
The people involved already knew this was not the intended way of working. They did not need another presentation explaining the rule. The bigger question was why the behaviour had become so normal that reporting every deviation seemed unrealistic.
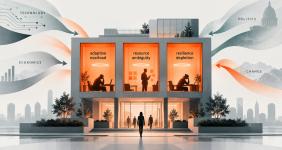
Security behaviour is shaped by more than knowledge. It depends partly on how practical the secure way of working is and what people learn from managers when delivery is under pressure or problems are raised. Security teams can write policies, build controls and provide training. They cannot shape all those conditions on their own.
When security rules make work harder
I saw this clearly during the pandemic when I was CISO at Örebro Municipality in Sweden. Before COVID we had spent considerable time discussing privacy, GDPR and the use of certain cloud services for sensitive personal information. Then the operating reality changed very quickly.
Municipal care staff still had to support older people while unnecessary hospital visits created another risk. Remote consultation became important almost overnight. We were concerned that if we did not provide a practical and approved way to communicate staff would eventually find their own. They would not have been doing that because they did not care about security. They would have been trying to care for people.
We carried out a rapid assessment and created a controlled exception with a clear routine for that situation. The security requirement had not disappeared. We had changed the conditions so that people had a workable way to meet it.
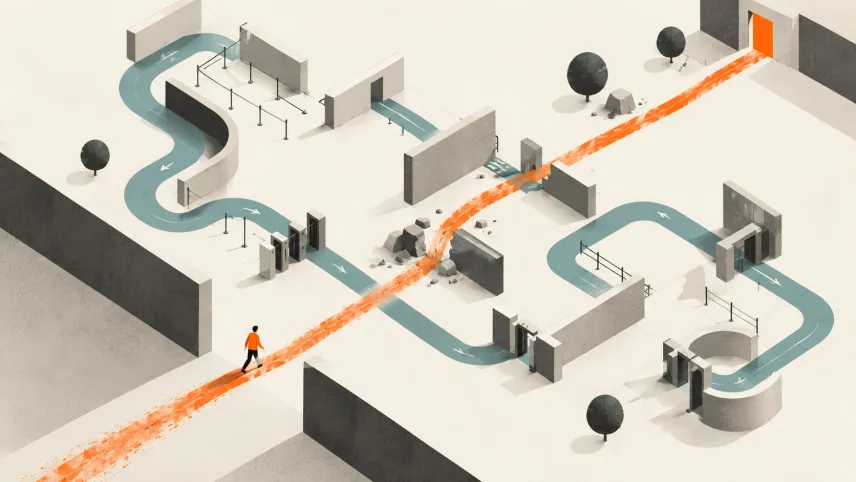
Organisations often tell employees what they must not do without asking whether the approved alternative actually works. When doing the job and following the security requirement repeatedly pull in opposite directions, somebody eventually has to choose. If that happens often enough, looking only at the employee who made the choice tells us very little about why the problem keeps returning.
How security shortcuts become normal
The phrase “everyone does it” should concern managers for another reason. Repeated deviations can change what people regard as normal.
A shortcut works once and nothing happens. It happens again. Colleagues see it being tolerated and over time the exception becomes part of the real process even though the written process has never changed.
A 2023 systematic review of 33 publications from high-risk industries identified production pressure, organisational factors and repeated exposure to risk without negative consequences among the factors associated with normalisation of deviance. The authors describe their framework as preliminary, but the underlying idea is useful here: repeated experience can change what people come to regard as acceptable.
By that point a reminder of the policy is competing with everyday experience. None of this removes personal responsibility. Some decisions are simply poor ones. But when the same behaviour keeps appearing across a team or organisation management should want to understand why.
If 10 people keep taking the same shortcut, investigating the shortcut may tell you more than training all 10 people again.
Why psychological safety matters when reporting security risks
Organisations have talked for years about open cultures, speaking up and learning from mistakes. Those ideas are easy to support when the information being reported is manageable.
The real test comes when somebody raises something that threatens a deadline or challenges an important decision.
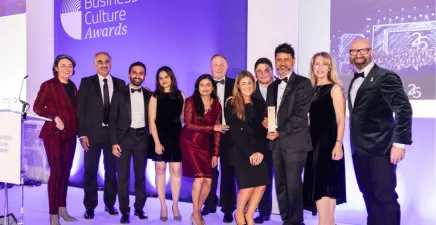
I experienced that directly during my time at the Swedish Transport Agency. I was one of four people in the security organisation selected to receive an external award recognising our work with governance, risk and compliance. Part of that work had involved bringing difficult security and governance issues connected with a major outsourcing programme to the surface.
Before the award ceremony we were told that accepting the award was inappropriate and could have formal consequences for us.
What stayed with me was not only what happened to those of us directly involved. It was the message that such an experience can send to everybody watching. Employees notice how colleagues are treated.
An organisation may say that raising risks is valued, but people will compare that statement with what happens when somebody reports a problem that delays a project or challenges an important decision. When the two messages conflict, what people see happening around them is hard to overcome with a policy or training session.
A 2026 study of 818 employees in Dutch governmental and semi-governmental organisations found psychological safety to be a strong independent predictor of whether employees intended to report suspected cyber incidents. The study measured intention rather than actual reporting – an important limitation – but it supports the point that people consider the consequences of speaking up.
A manager's first response to bad news therefore matters. Someone who says “I think I made a security mistake” is watching what happens next, and the people around them are watching too. If the first reaction is irritation or blame, people remember it. A manager who first tries to understand what happened creates a different experience.
There still has to be accountability. Deliberate misconduct is different from making a mistake or reporting a concern in good faith. Organisations need to be able to tell the difference.
Why cybersecurity training alone cannot change behaviour
Security awareness remains necessary. If somebody does not understand how sensitive information should be handled, training may be exactly what is needed. The problem comes when people already know the rule.
Training is attractive partly because it is easy to document. Organisations can show who completed a course or passed a test while changed behaviour is much harder to demonstrate.
If the approved way of working repeatedly makes the job harder, another course does not change the process. If experience has taught people that difficult news brings personal trouble, another reminder to report incidents will not remove that concern.
Security also needs to become part of ordinary conversations about work. A team might occasionally ask: “What did we do recently that did not work as safely as we intended?”
The purpose is not confession. It is to find where the way work is organised makes unwanted behaviour more likely. Mistakes and near misses can provide useful information if the organisation is prepared to learn from them.
How HR and managers shape security culture
HR should not take over responsibility for cybersecurity. But HR and people teams influence several of the conditions that determine whether security policies actually work in practice.
Performance management is one example. If a manager is judged mainly on output and meeting deadlines, that matters when a security requirement slows delivery. The policy may say one thing while the way performance is assessed encourages something else.
HR can also look at how managers deal with difficult information. Is somebody who raises a problem that delays delivery seen as acting responsibly or as getting in the way? When an employee reports a mistake, does the conversation begin by trying to understand what happened or by deciding who is at fault?
Managers teach through their own behaviour as well. If leaders regularly bypass a security process because they are busy, employees notice. If a manager supports somebody who stops a process because something looks wrong, people notice that too. This does not require a reward scheme or another campaign. Sometimes reinforcement is simply making clear that stopping and checking was the right thing to do.
Incident investigations are another opportunity to learn. Knowing who made an error may be necessary, but it should not always be the final answer.
Was the approved process realistic? Had the same workaround appeared before? Did managers know it was happening? Was something about the workload or the tool making the deviation more likely?
Asking those questions is not about excusing the individual. It is about finding out whether the organisation has allowed the same problem to repeat.
Three questions HR leaders should ask about security behaviour
Completion rates and incident statistics still have value. They just do not tell the whole story.
I would want an HR director, CISO and operational manager to be able to discuss three other questions:
- Where does our way of working create incentives to bypass security requirements?
- What actually happens to somebody who reports a problem that may delay delivery?
- Which deviations have become so common that people no longer react to them?
The answers may point back towards management rather than towards the employee who clicked the wrong link or broke the rule. That is precisely why they are useful.
If people already know the rule and still find themselves breaking it every week, the first question should not be how to explain the rule again. It should be what in the organisation keeps making the unsafe choice easier or less costly than the secure one.
About the author